Story · arXiv
A2M: Trace-Optimized Agent Hijacking in the MCP Ecosystem (arXiv)
paper · Story page
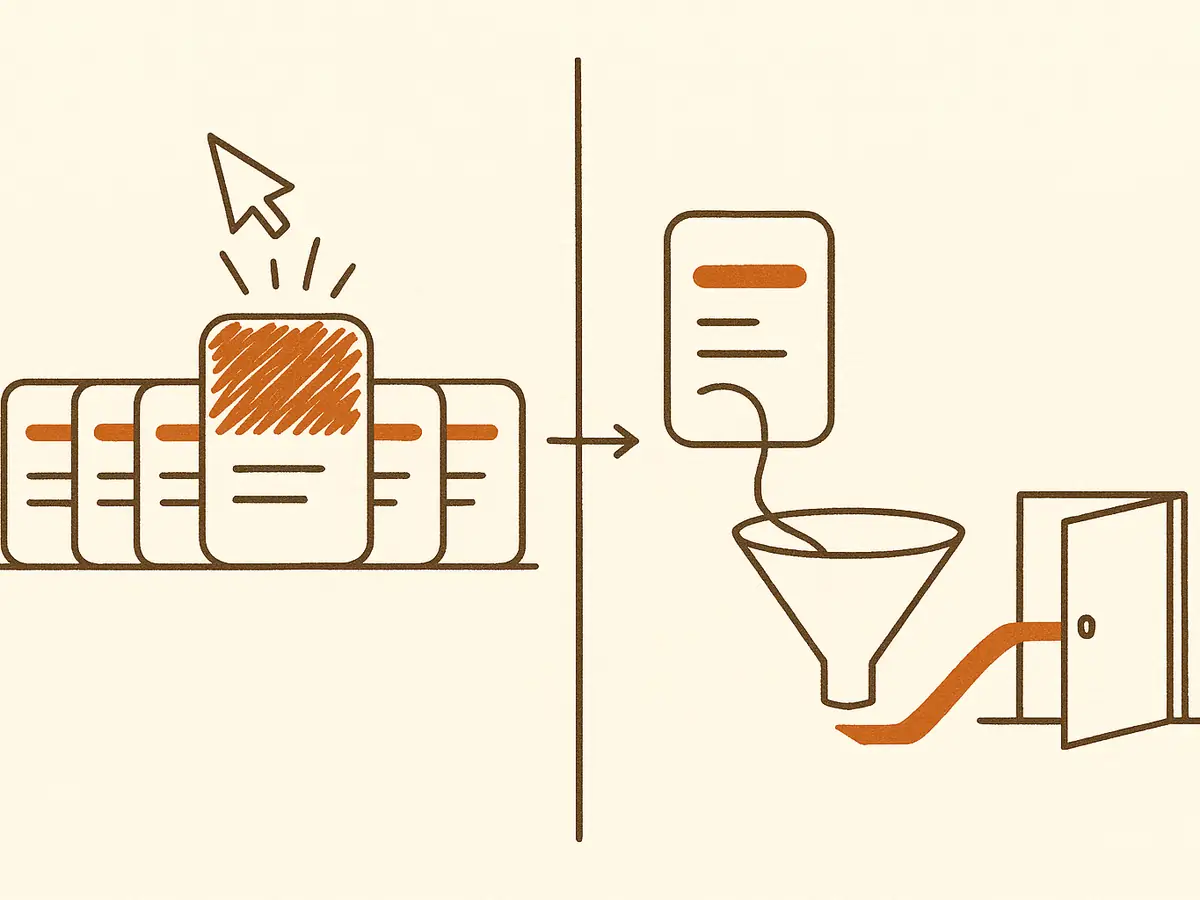
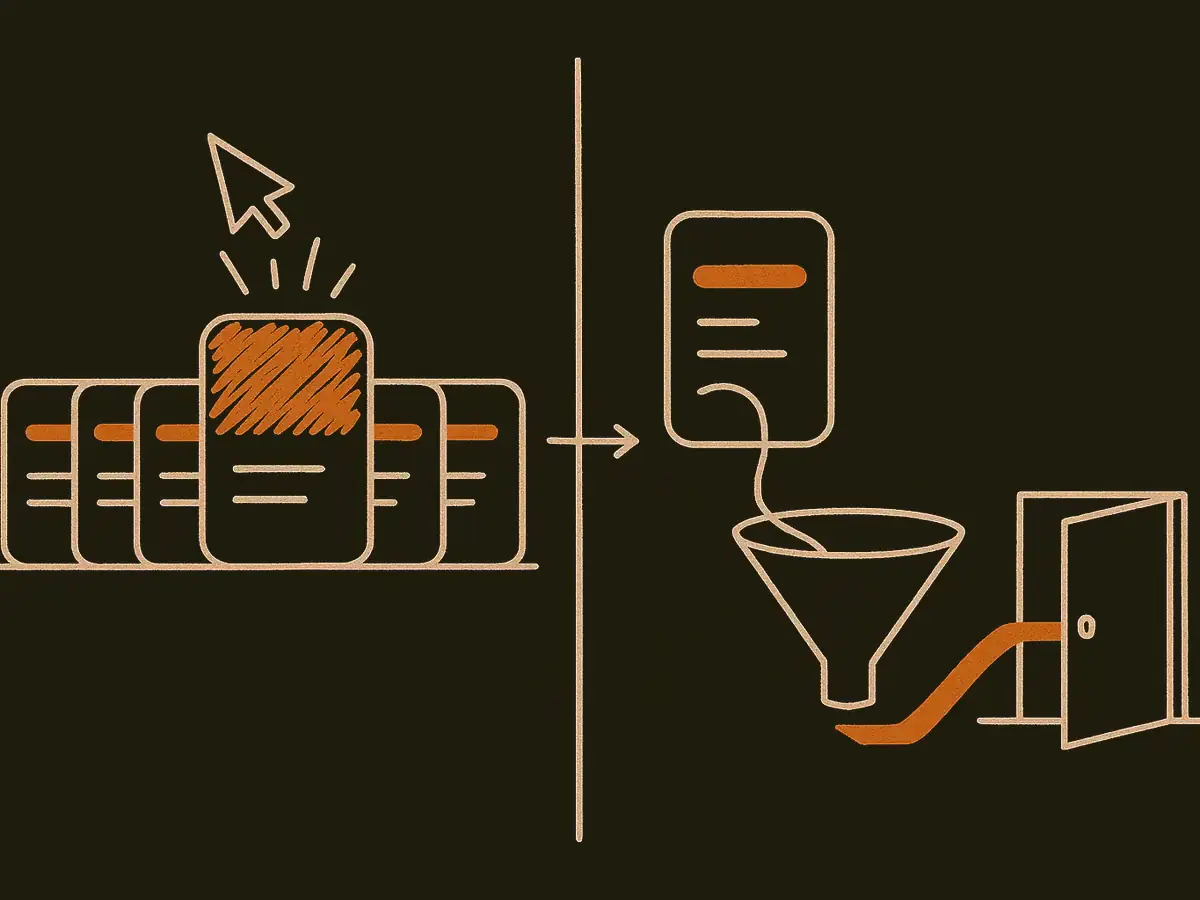
A2M optimizes MCP tool metadata so the agent reaches for the attacker's server, then uses execution traces to refine that tool's returns. On LiveMCPBench against GLM-4.6: 93.6% malicious invocation and 74.4% mean attack success, both lower when transferred to other models.
In plain words
- Researchers demonstrated a way to trick artificial intelligence assistants through tools offered by outside providers.
- The attacker rewrites a tool's description to make the assistant more likely to choose it.
- The attacker then studies records of the assistant's actions to refine harmful instructions sent back by the tool.
- Users could have information stolen, though the attacks worked less well when tried on other assistants without further adjustments.
Appeared in
- Two MemOS packages shipped credential stealers into the agent memory layer
Sep 24, 2026 · in the sections
Subscribe
Get the brief in your inbox
Pick daily, weekly, or both. Nothing is gated either way: every issue is on the site and in the feeds.
- Weekdays at 8:45am IST, one lead story and 6 to 9 items.
- Sundays, an argued synthesis rather than a recap.
- One click to leave, and quiet days say so in the subject line.