Story · Vercel
A sandbox without a network boundary is only half a sandbox (Vercel)
blog post · Story page
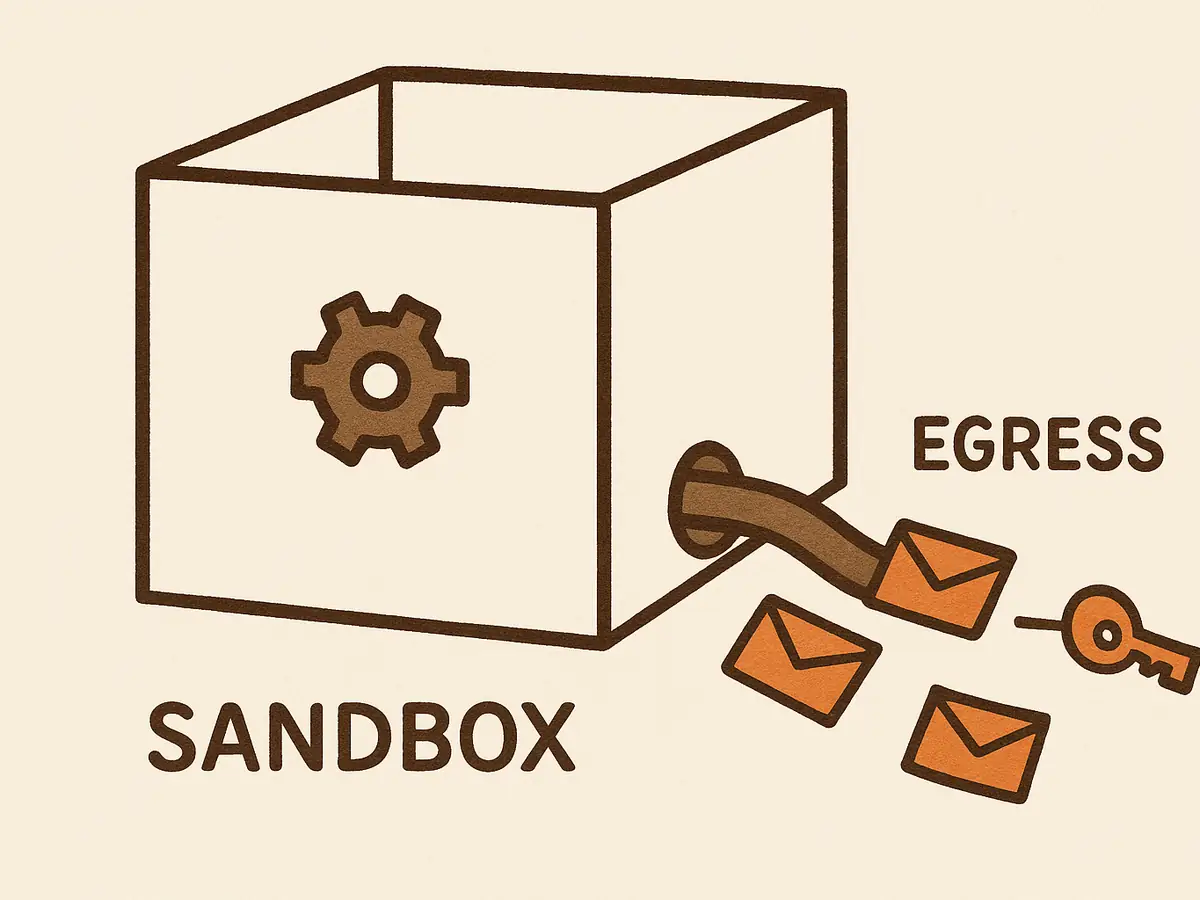
Vercel's argument: isolation without egress control "contains the process, not its consequences." A microVM can't stop agent-run code from exfiltrating data or abusing credentials over the network, so egress rules, credential controls, and lifecycle-aware network permissions belong inside the sandbox's security boundary.
In plain words
- Vercel says separating potentially harmful code from a computer is not enough unless its network access is controlled too.
- A small computer created inside a larger computer can contain dangerous code, but it cannot prevent connections to other systems.
- Those connections could send out private data, search internal services for weaknesses, attack outside systems, or misuse stored login details.
- The protected environment needs rules for where code may connect, which login details it may use, and when permissions change.
- Teams letting artificial intelligence run code need these controls to limit damage beyond the computer running it.
Appeared in
- Claude Code turns auto mode on for everyone; reward-hack monitors catch 28%
Aug 11, 2026 · in the sections
Subscribe
Get the brief in your inbox
Pick daily, weekly, or both. Nothing is gated either way: every issue is on the site and in the feeds.
- Weekdays at 8:45am IST, one lead story and 6 to 9 items.
- Sundays, an argued synthesis rather than a recap.
- One click to leave, and quiet days say so in the subject line.